data protection officer recruitment agency and headhunters
your next DPO, in good hands.
We combine our data, our sector experts and our AI algorithms to identify the headhunter most relevant to your role, from a first DPO in an SME to a DPO shared across multiple structures.
- no setup fees, pay on hire
- guaranteed replacement
they hire their data protection profiles with muzzo
how do you hire a DPO through a recruitment agency?
A DPO keeps a processing register real, not just a GDPR document. Muzzo gives your role, from a first DPO in an SME to a group DPO, to the headhunters who place this job most: they test a DPIA already conducted. Fee of 5 to 30%, paid on hire. Leaves within 3 months: we restart free.
how it works
you only pay if you hire
01
you describe the role
Using the form above: the role, your company, the number of organisations to cover. The rest is scoped in your first conversation with the Muzzo team.
02
our data chooses the headhunters
Our AI picks those who have hired the most DPO, from more than 2,500 selected headhunters.
03
you meet the best profiles
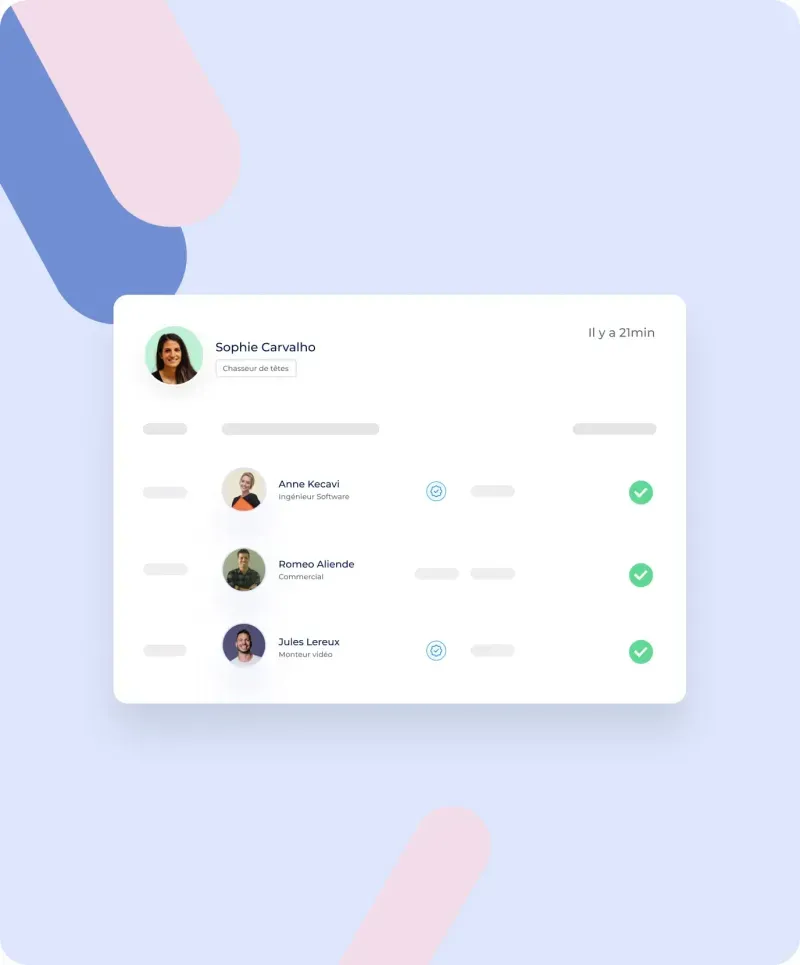
Approached and qualified by headhunters who are data protection experts. You choose who you meet.
04
you hire, then you pay
Not before. If your new hire leaves within 3 months, we restart the search at no cost.
they hired with muzzo
Muzzo's strength is the diversity of its recruiters: there is always someone listening to our needs.
With Muzzo, I get the reactivity of a marketplace and the quality of a search firm.
let's talk about your role
Antoine and the Muzzo team help you scope your role and choose the right headhunters. Describe your role in the form: we'll call you back to discuss it.
Antoine GigomasCEO and co-founder of Muzzo
one last question?
With Muzzo, you set the fee, between 5 and 30%, and you only pay it on hire: no deposit, no fixed fees. A first DPO in an SME and a group DPO consolidating multiple subsidiaries do not call for the same search. The fee follows that difficulty, and the Muzzo team helps you set it.
You have a double guarantee. If your new hire leaves within 3 months, for example because the actual scope does not match the brief, we restart the search at no cost. If we find no replacement within 4 months, we refund 50% of the fees. On average, 94% of Muzzo hires are still in post after 3 months.
data protection headhunters are ready to start
A hire signed in under 26 days, paid only when you hire.
the reality
a DPO is judged by the register they keep, not by their CV
a good DPO is busy with a DPIA, not reading job ads
They update the processing register, run a DPIA or answer a CNIL request. They are not looking for a job. A data protection headhunter knows when and how to approach them.
a GDPR certificate does not make an operational DPO
The role means having business teams adopt data protection rules even when they do not see the point. The headhunter tests this dialogue, not just mastered texts.
a hiring mistake shows up at the first data breach
Incomplete register, DPIA never run, notification to CNIL late. The headhunter checks the registers kept and DPIA actually conducted before introducing anyone.
the roles
the data protection profiles our headhunters go after for you
From a first DPO in an SME to a DPO shared across structures, each search goes to a headhunter who has already hired that profile.
internal DPO
Designated under GDPR articles 37-39, they keep the processing register, run DPIA and answer CNIL for a single organisation.
shared DPO
They carry the role for multiple organisations at once, often in a group, franchise or association network. Fast-growing format.
group DPO
They consolidate the processing register of multiple subsidiaries and align data protection procedures across the group.
first DPO in an SME
They structure the role from scratch, often alongside another job, and must convince a leadership discovering GDPR obligations.
GDPR lead before formal designation
Before appointing a formal DPO, some companies hire a lead to prepare compliance and the processing register.
DPO in a regulated sector
In banking, insurance or healthcare, they align GDPR with other regulatory obligations, often closely with the CISO.
the method
a data protection headhunter, not a general legal agency
A DPO is judged by the register they keep and the DPIA they run. So the method starts from that scope.
we define the GDPR scope to cover
Number of processing activities, organisations to cover (single or multiple through sharing), existing relation with CNIL: the brief describes the actual scope of the role.
a headhunter who places DPO
From more than 2,500 selected headhunters, your role goes to those who place the most people in data protection.
a DPIA verified before the interview
The headhunter asks the profile to walk them through a DPIA or data breach they managed: the method followed, the decision taken, what leadership made of it. Then they cross-check with references.
the figures
a DPO in figures
34,440
DPO designated with CNIL as of early 2024, up from 21,000 in 20191
57%
of internal and shared DPO work in organisations with fewer than 250 employees, up 19 points since 20192
49%
of IT security managers (family which lists the DPO) have variable pay, €4,000 median3
€76k
median salary in banking and insurance for the same family (80% between €53k and €115k), where the DPO is often full-time3
- DGEFP, CNIL and AFCDP, press release, DPO profession observatory, 2024 edition (opens a new window), 2024 data
- CNIL, the data protection officer: an increasingly represented profession in small organisations, DGEFP/CNIL/AFCDP observatory (opens a new window), 2024 data
- Apec, managerial remuneration in the private sector across 111 job families, 2025 edition, p. 56 (IT security) (opens a new window), 2025 data
hiring a DPO: what you need to know
The DPO, designated under GDPR articles 37-39, keeps the processing register, runs DPIA and answers CNIL. Good profiles are in post, busy with ongoing compliance, and do not answer job ads.
A data protection headhunter knows how to approach them and ask the right questions: how many organisations to cover, what volume of processing, what relation with CNIL. This page covers the DPO role itself; for IT security as a whole, see our CISO page.
An internal DPO carries the role for a single organisation. A shared DPO splits it among several entities, often in a group or association network. This setup is growing fast: per the DGEFP/CNIL/AFCDP observatory, 57% of internal and shared DPO now work in organisations with fewer than 250 employees, up 19 points since 2019.
Choose the format before discussing salary: a shared DPO across multiple structures calls for different organisation and availability than one dedicated to a single entity.
The CV lists GDPR certifications and mastered texts. The interview must show something else: the ability to have business teams adopt data protection rules under pressure, and to document a file to withstand a CNIL inspection.
A short case study works well: a high-risk processing activity, time to explain how to run the DPIA it calls for. The headhunter does this first screen before introducing anyone, and checks with references the registers and DPIA the profile says they conducted.
why is the DPO role growing so fast?
The number of DPO designated with CNIL has grown sharply: per the same study, it went from 21,000 in 2019 to 34,440 as of early 2024. The role is also spreading by organisation size, with sharp growth in organisations with fewer than 10 and 10 to 49 people.
This growth hits hiring directly: experienced profiles, trained in GDPR for years, stay rarer than the demand for roles.
In a company designating its first DPO, the role often starts from zero: no formal register, processing scattered across teams, a leadership discovering GDPR obligations. You need an autonomous profile, able to build the tools and set priorities.
In a group, the DPO consolidates the register from multiple subsidiaries and aligns procedures already in place elsewhere. Per Apec, for the family which lists the DPO, salary is highest in banking and insurance, €76k median, where regulatory obligations on data are strongest.
your questions about hiring a DPO
Per the DGEFP/CNIL/AFCDP observatory, 34,440 DPO were designated with CNIL as of early 2024, up from 21,000 in 2019. The role is also spreading among small organisations: 57% of internal and shared DPO work in organisations with fewer than 250 employees.
Apec does not publish a DPO-only range, but the IT security family which lists them shows higher salary in banking and insurance, €76k median, and variable pay among 49% of managers, €4,000 median (2025 edition).
The DPO ensures GDPR compliance for personal data processing: register, DPIA, relation with CNIL. The CISO leads the security of the whole IT system, well beyond personal data alone. For that role, see our CISO page.
Yes, it is even the most common setup for small organisations: GDPR allows a shared DPO among multiple entities, for example in a group or association network. Specify in the brief how many organisations to cover; it changes the profile you need.
With a real case rather than a list of certifications. Our headhunters ask the profile to walk through a DPIA or data breach they managed, and check with references the registers and analyses they mention.
by Antoine Gigomas, CEO and co-founder of Muzzo ·